This guide outlines the steps to configure Single Sign-On (SSO) with Okta for Qualified. Follow these instructions to streamline authentication for your users and enhance security.
Prerequisites
- Access to the Okta Admin Console with super admin access.
- Access to Qualified’s Enterprise Single Sign-On and the Admin user role.
- Your organization’s Company ID from Qualified.
- A basic understanding of SAML 2.0 configuration.
Steps to configure Okta SSO
Step 1: Set up in Qualified
- Log in to your Qualified Admin account.
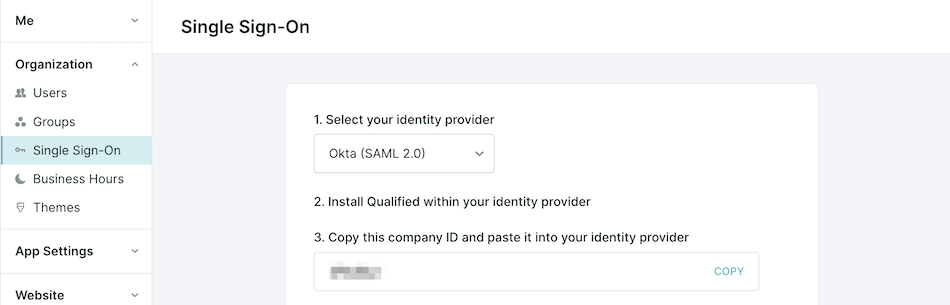
- Navigate to Settings → Organization → Single Sign-On.
- Select Okta (SAML 2.0) from the dropdown menu.
- Copy your Company ID.
Step 2: Configure in Okta
- Log in to the Okta Admin Console.
- Go to Applications → Applications, and click Add Application.
- Search for the Qualified app (not Qualified.io) and click Add Integration.
- Keep the default application label, or customize it, and click Done.
- Within the application, click on the Sign On tab, and then click Edit.
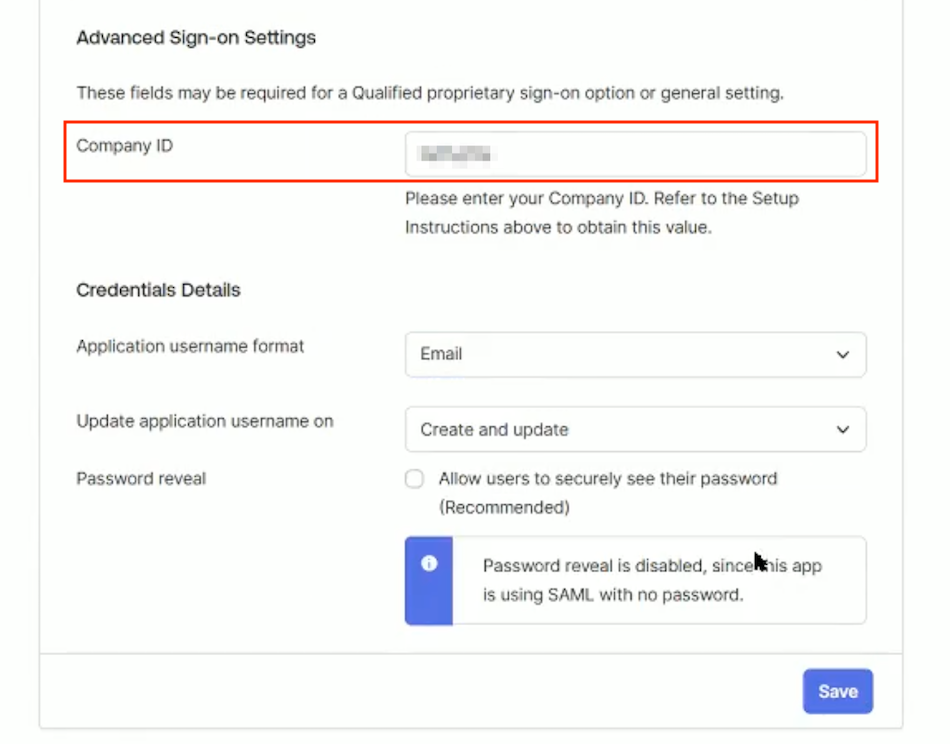
- Scroll down to the Advanced Sign-on Settings section and paste in the Company ID that you copied from Qualified, and click on Save.
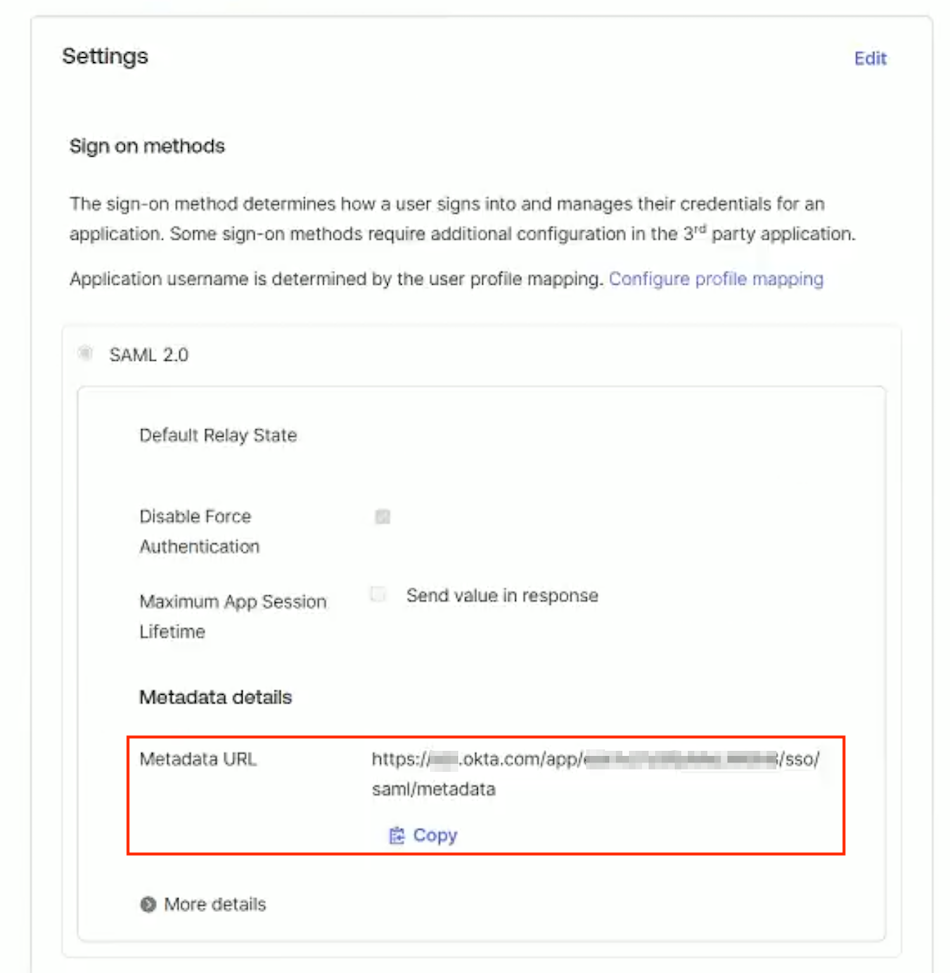
- Then, scroll back up to copy the Metadata URL.
Okta Documentation: Add existing app integrations
Step 3: Finalize SSO in Qualified
- Return to Settings → Organization → Single Sign-On in Qualified.
- Paste the Identity Provider metadata link from Okta into the required field.
- Click Save and then Verify Configuration to test the connection.
- Before enabling single sign-on, make sure to assign all existing Qualified users access to the Qualified application in Okta (including yourself) as they will no longer be able to access Qualified with their password once SSO is enabled.
- Existing users will receive an email to bind their accounts.
- When you’re ready, click Enable single sign-on for this org.
Multiple Qualified orgs on one identity provider
If your company has more than one Qualified org, you can connect each of them to the same Okta tenant. Each Qualified org needs its own app integration in Okta.
-
First org: Follow the steps above as written, using the Qualified app from the Okta catalog.
-
Each additional org: The catalog app’s Entity ID can’t be edited, so create a custom SAML 2.0 app integration for the org instead. Set its Entity ID to
https://app.qualified.com/[PASTE_YOUR_COMPANY_ID_HERE], using that org’s Company ID from Settings → Organization → Single Sign-On.
Request to enable: Contact your Qualified Success Architect before you set up SSO for an additional org. Qualified turns on the new Entity ID format for that org.
Enable SCIM provisioning (optional)
SCIM provisioning in Okta automates user management tasks such as creating, updating, and deactivating users in Qualified.
Supported provisioning features
The following provisioning features are supported within Qualified provisioning of SSO users:
- Push new users: New users created in Okta are automatically created in Qualified. When a user is provisioned, their name, job title, profile (role), phone number, email, and timezone are synced.
- Push profile updates: Changes to a user's email or Qualified Role in Okta are pushed to Qualified. Other details, such as name, job title, and phone number, are set when the user is created and aren't updated afterward.
- Push user deactivation: Deactivating a user in Okta will deactivate the user in Qualified. This removes their login access but retains their information.
- Reactivate users: User accounts can be reactivated in Qualified directly from Okta.
Using custom user profiles with SCIM
In addition to the default roles, Qualified's User Profiles feature allows you to create custom permission sets. You can sync these custom profiles via SCIM by adding values to the Qualified Role attribute in Okta that match each profile's unique API Name in Qualified. The steps are in Steps to Enable SCIM Provisioning below.
Note: A profile's API Name must be all lowercase with no spaces, for example
sales_manager. Qualified doesn't show an error when an API Name is formatted incorrectly, and a profile with a badly formatted API Name won't sync from Okta. Check the API Name in Qualified before you add it to Okta.
For full details on creating custom profiles and finding their API Name, see How to manage users in Qualified.
Steps to enable SCIM provisioning
Step 1: In Qualified
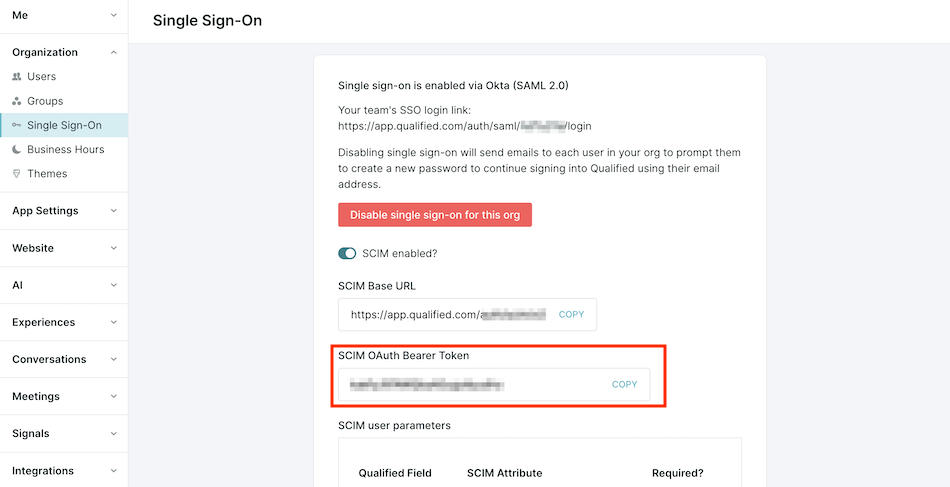
- Go to Settings → Organization → Single Sign-On.
- Toggle on SCIM Enabled to enable SCIM provisioning.
- Copy the SCIM OAuth Bearer Token displayed on the screen.
Step 2: In Okta
- Log in to your Okta Admin console.
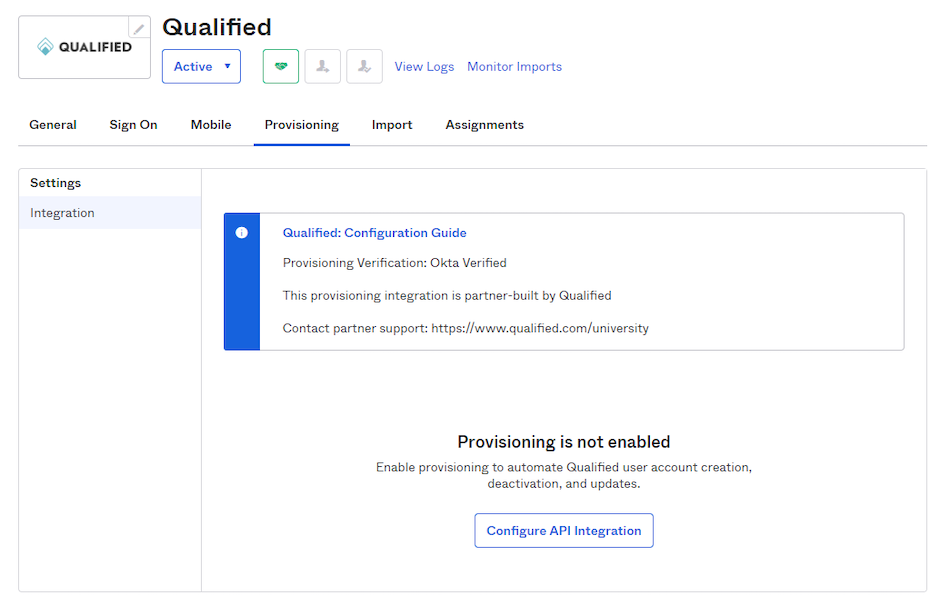
- Go to the Applications section and open the Qualified application.
- Click the Provisioning tab, then click Configure API integration.
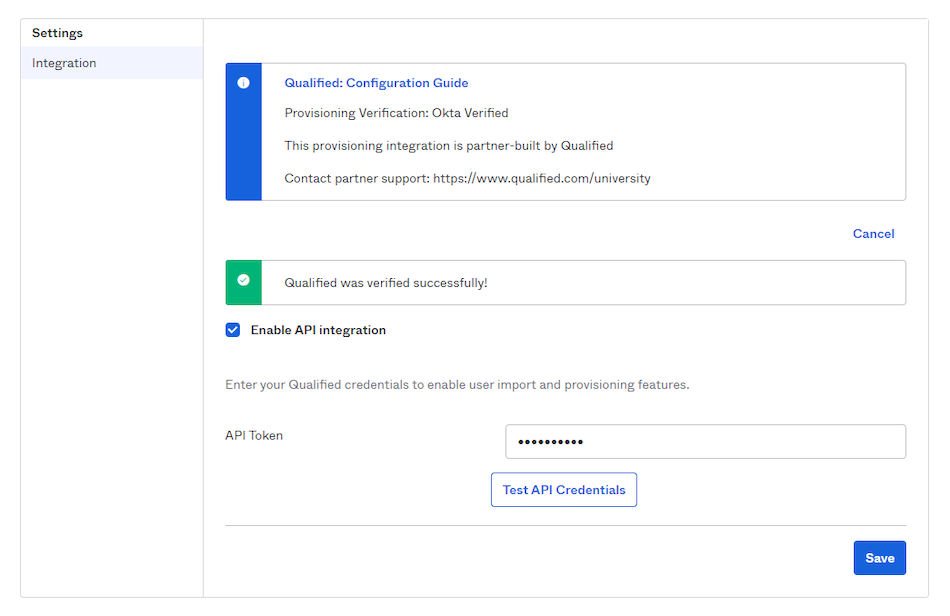
- Enable the API Integration checkbox.
- Paste the Bearer Token from Qualified into the OAuth Bearer Token field.
- Click Test API Credentials to verify the connection.
- Click Save.
- Enable provisioning actions
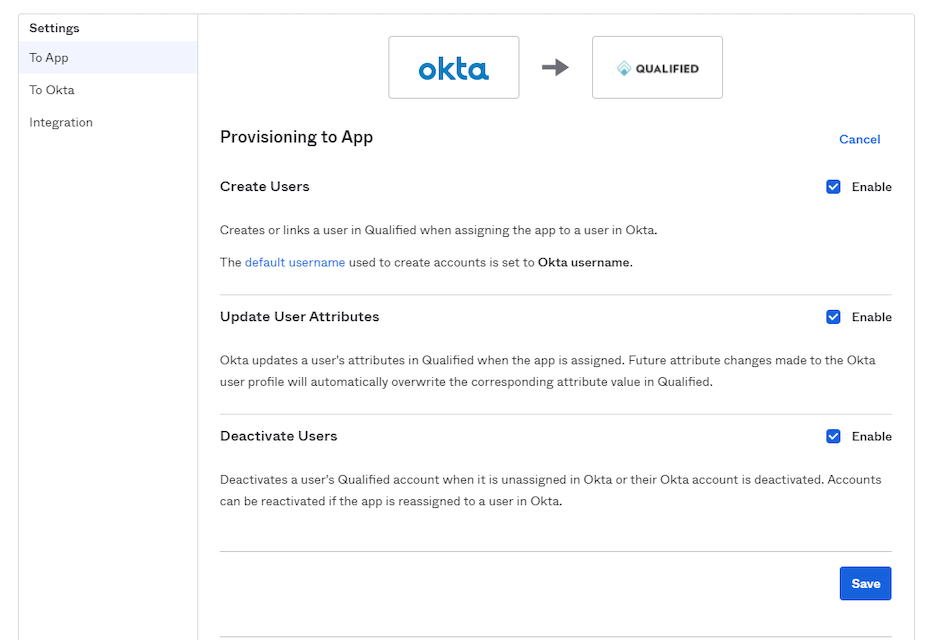
- Under the Provisioning tab, click To App and then Edit.
- Check the boxes to enable:
- Create Users
- Update User Attributes
- Deactivate Users
- Scroll down to the Attribute Mappings section and click Go to Profile Editor.
-
Find the "Qualified Role" attribute and click the pencil icon to edit it.
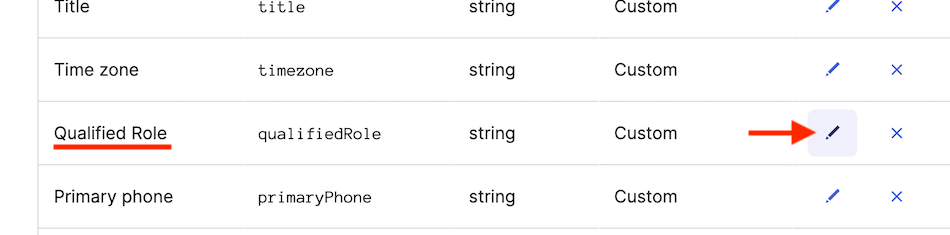
- Under the "Attribute members" section, you will add values that correspond to your Qualified User Profiles. By default, "Admin" and "Rep" are included. "Rep" uses the value
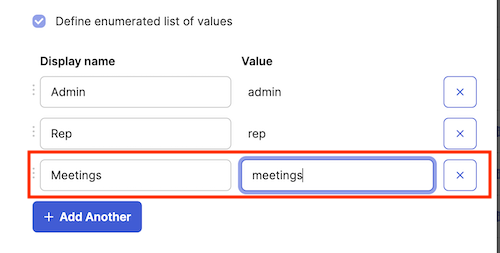
chat, which assigns the Chat profile in Qualified.- To add the default Meetings profile, click + Add Another and enter:
- Display Name: Meetings
- Value:
meetings(case-sensitive)
- To add a custom profile, click + Add Another and enter the profile's name and API Name. For example:
- Display Name: Sales Manager
-
Value:
sales_manager(This must exactly match the API Name in Qualified, and be all lowercase with no spaces)
- To add the default Meetings profile, click + Add Another and enter:
- Click Save Attribute.
Okta Documentation: Add SCIM provisioning to app integrations
Step 3: Testing and verification
- Add a test user in Okta and assign them to the Qualified application with one of the configured roles.
- Verify the user is created in Qualified with the correct attributes and profile.
- Update the test user's attributes (e.g., role or email) in Okta and confirm the changes sync correctly in Qualified.
- Deactivate the test user in Okta and ensure their access is removed in Qualified.
Binding email process for existing users
After enabling SSO, all existing Qualified users receive an email from app@qualified.com with a unique binding link.
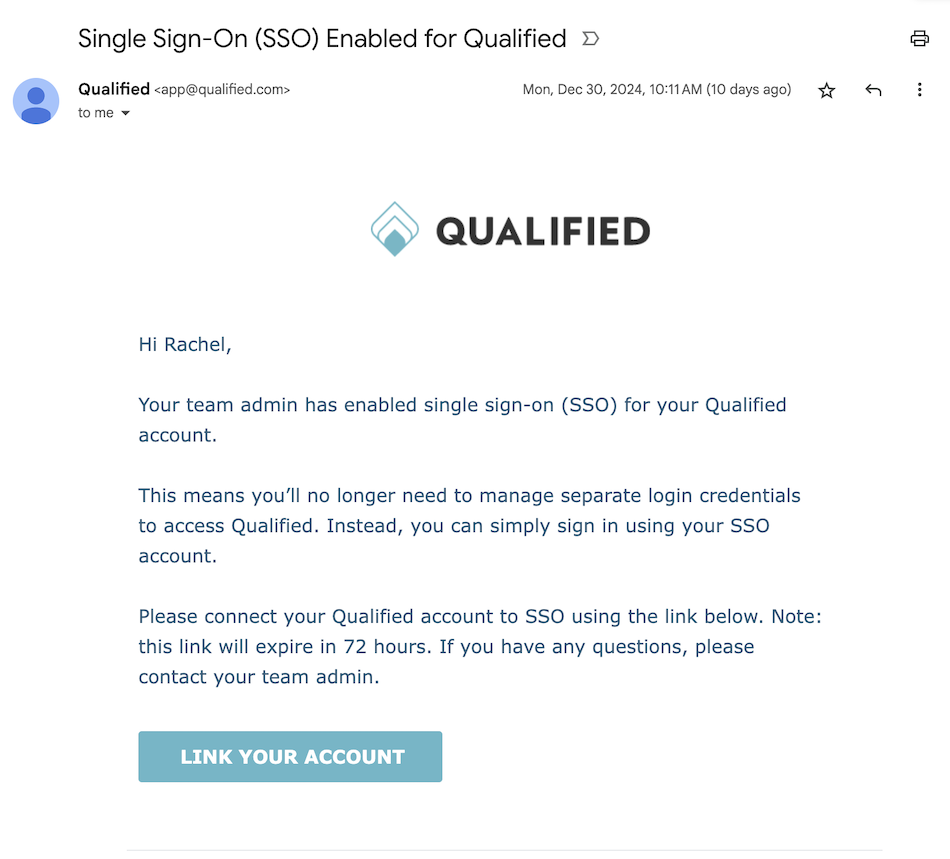
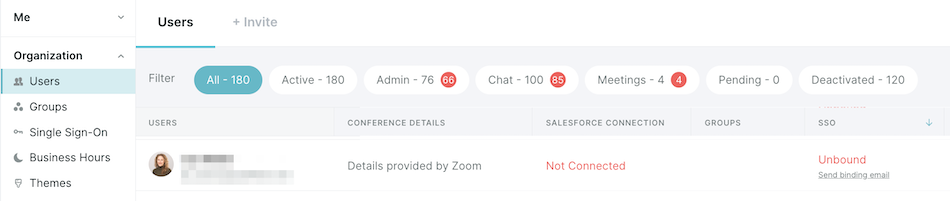
Users must click the link within 72 hours to bind their Qualified account to their Okta Account. If the binding link expires, an admin can resend it from Qualified by going to Settings → Organization → Users.
Adding new users
With SCIM provisioning enabled
An Okta admin assigns the user to the Qualified app with the appropriate Qualified Role attribute: Admin, Rep (the Chat profile), Meetings, or the API Name of a custom profile.
To provision a whole group instead, open the group in Okta, go to its Applications tab, click Assign Application, and assign the Qualified app. Select the Qualified Role for the group, then add users to the group.
Users added through SCIM don't receive a binding email. They sign in from the Qualified SSO page or directly from Okta.
Okta Documentation: Assign app integrations
Without SCIM provisioning
If SCIM provisioning isn’t enabled, follow these steps to add new users to Qualified:
- Assign users in Okta: An Okta admin assigns the user to the Qualified application in Okta. See Assign app integrations.
- Invite users in Qualified: Invite users from Settings → Organization → Users. See How to manage users in Qualified.
- User accepts invite: Invited users will receive an email with a button to link their account and access Qualified.
Disconnecting SSO
If you'd like to disconnect your company’s SSO, you can do so at any time.
- Go to Settings → Organization → Single Sign-On
- Click Disable SSO for this team.
- Users will receive an email to create a new password and log in using their email addresses.